Why Website Performance Is a Security Indicator, Not Just a User Experience Metric
CybersecurityIntroduction
Website performance is typically measured through the lens of user experience. Faster pages improve search rankings, reduce bounce rates, and increase conversion rates. As a result, performance optimization is often viewed as a marketing or frontend engineering concern rather than a cybersecurity issue.
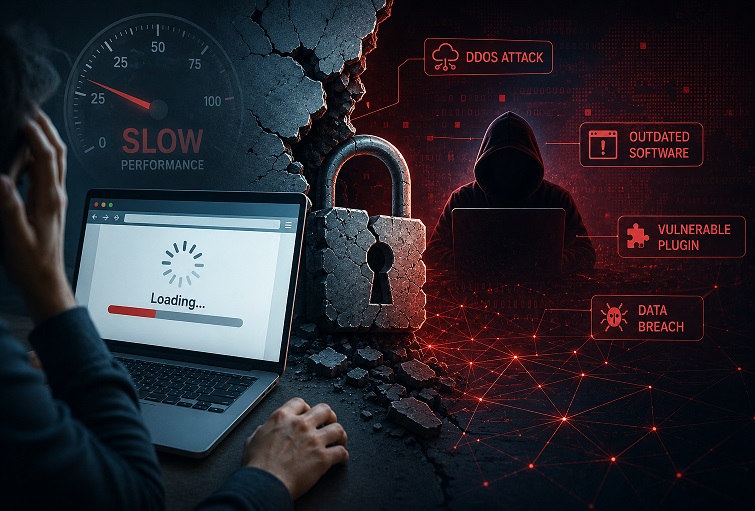
In practice, however, application performance and security are closely connected. The same architectural weaknesses that introduce latency frequently expand the attack surface, while many active cyberattacks first reveal themselves as performance degradation before triggering conventional security alerts.
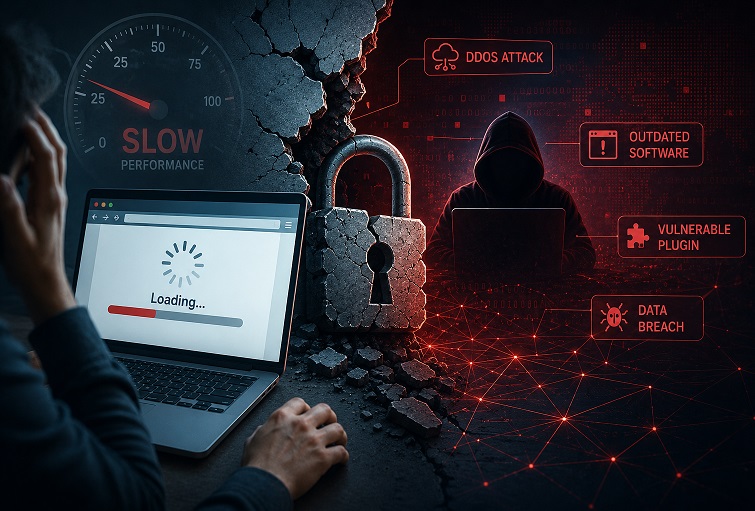
Modern web infrastructure should therefore treat abnormal response times as operational signals rather than isolated performance problems. A slow application may indicate inefficient code, but it may also point to vulnerable software components, malicious traffic, resource exhaustion, or an ongoing attack.
Organizations that evaluate performance and security together are generally able to detect infrastructure problems earlier and reduce overall operational risk.
Performance and Security Share the Same Technical Foundation
Website performance depends on every layer of the application stack, including the operating system, runtime environment, web server, application framework, database, network infrastructure, and third-party services.
Security depends on exactly the same components.
As software systems age, they gradually accumulate technical debt. Legacy frameworks, unsupported plugins, obsolete libraries, and outdated runtime environments increase execution overhead while simultaneously exposing known vulnerabilities.
This relationship explains why performance optimization projects often uncover security issues, and security assessments frequently identify inefficient application architecture.
A server running an outdated PHP version, an obsolete Java runtime, or an unsupported content management system is likely to exhibit both slower execution and greater exposure to publicly documented exploits.
Keeping software current therefore improves more than security posture. It often produces measurable gains in application responsiveness, memory efficiency, and resource utilization.
Outdated Components Increase Both Latency and Risk
Modern applications rely heavily on open-source software.
A typical web application may contain hundreds or even thousands of third-party dependencies distributed across backend services, frontend frameworks, analytics tools, and build pipelines.
Every dependency introduces two potential problems.
The first is performance overhead. Older libraries often execute inefficiently, increase bundle sizes, or require unnecessary network requests.
The second is security exposure.
Cybercriminals continuously scan internet-facing systems for known software versions associated with publicly disclosed vulnerabilities. Automated vulnerability scanners can identify outdated frameworks within seconds, allowing attackers to launch exploits with little manual effort.
Many high-profile security incidents have followed this pattern.
The 2017 Equifax breach, for example, resulted from an unpatched vulnerability in the Apache Struts framework. Although the vulnerability had already been publicly disclosed and patches were available, the affected systems remained outdated long enough for attackers to compromise sensitive customer data.
Such incidents demonstrate that software maintenance is both a performance and a security requirement.
Performance Degradation Can Reveal Active Attacks
Not every slowdown originates from inefficient software.
Performance anomalies frequently represent the first observable symptom of malicious activity.
Distributed Denial-of-Service (DDoS) attacks intentionally overwhelm servers with excessive traffic, exhausting CPU resources, memory, bandwidth, or connection pools until legitimate users experience severe latency or complete service disruption.
While large-scale DDoS attacks attract media attention, smaller resource exhaustion attacks have become increasingly common against businesses of all sizes.
Similarly, credential stuffing attacks, brute-force authentication attempts, aggressive web scraping, and automated reconnaissance generate sustained traffic that gradually consumes server resources without necessarily triggering immediate security alarms.
From an operational perspective, unexplained increases in response time, CPU utilization, or request volume should be investigated as potential security events rather than assumed to be ordinary traffic fluctuations.
Performance monitoring systems can therefore serve as an additional layer of threat detection when integrated with security operations.
Resource Exhaustion Is Not Always Obvious
Many attacks deliberately avoid overwhelming infrastructure.
Instead, they consume resources gradually while remaining below traditional alert thresholds.
Attackers may repeatedly execute expensive database queries, abuse search functionality, generate excessive API requests, or trigger computationally intensive application workflows.
Each request appears legitimate when viewed individually.
Collectively, however, they increase latency, reduce server capacity, and create favorable conditions for additional attacks.
Because these techniques resemble normal user behavior, they often remain undetected unless performance telemetry is analyzed alongside security logs.
Observability platforms that combine application metrics, infrastructure monitoring, and security analytics provide significantly greater visibility into these subtle attack patterns.
Poor Performance Can Introduce New Security Weaknesses
Website latency influences not only infrastructure but also user behavior.
When applications respond slowly, users frequently submit forms multiple times, refresh pages repeatedly, or abandon transactions before completion.
These behaviors complicate fraud detection, increase duplicate requests, and create inconsistencies within backend systems.
Operational teams also face pressure to reduce latency.
Security mechanisms perceived as performance bottlenecks are sometimes weakened or disabled entirely. Organizations may reduce logging, simplify authentication workflows, relax Web Application Firewall rules, or bypass security inspections in an effort to improve page speed.
While these changes may produce modest performance gains, they frequently reduce overall resilience against attack.
Another common consequence involves session management.
Applications suffering from long response times often extend session lifetimes to improve user experience. Longer session durations, however, provide attackers with larger windows for session hijacking and credential misuse.
Performance optimization should never come at the expense of fundamental security controls.
Shared Optimization Strategies
Fortunately, many improvements strengthen both performance and cybersecurity simultaneously.
Keeping operating systems, application frameworks, and software dependencies fully patched removes known vulnerabilities while improving execution efficiency.
Reducing unnecessary JavaScript libraries and third-party integrations decreases page weight, shortens load times, and minimizes external attack surfaces.
Content Delivery Networks (CDNs) improve performance by caching static resources closer to end users while simultaneously absorbing malicious traffic before it reaches origin servers.
Rate limiting protects applications against abusive clients while preserving server resources for legitimate users.
Caching reduces backend workload and increases resilience during traffic spikes.
Load balancing distributes requests efficiently across infrastructure while improving availability during hardware failures or attack scenarios.
Modern edge security platforms increasingly combine these capabilities into unified architectures that optimize both speed and resilience.
Performance Monitoring as a Security Control
Traditional monitoring focused primarily on uptime and infrastructure health.
Today, observability platforms collect a much broader range of telemetry, including request latency, application traces, API usage patterns, user behavior, and infrastructure metrics.
When correlated with authentication logs, firewall events, and endpoint telemetry, these datasets provide valuable security intelligence.
Unexpected latency affecting specific endpoints may indicate targeted reconnaissance.
A sudden increase in failed login requests may precede credential stuffing attacks.
Elevated database execution times may reveal malicious query patterns.
Rather than operating independently, performance monitoring and security monitoring increasingly complement one another.
Organizations adopting integrated observability platforms are often able to identify abnormal behavior significantly earlier than those relying solely on conventional security alerts.
Building Secure and High-Performance Applications
Performance optimization should be incorporated into broader security engineering practices rather than treated as a separate initiative.
Effective strategies include:
- maintaining an aggressive software patching policy;
- minimizing third-party dependencies;
- implementing continuous vulnerability scanning;
- monitoring infrastructure and application performance in real time;
- deploying Web Application Firewalls and intelligent rate limiting;
- using Content Delivery Networks to reduce origin exposure;
- continuously analyzing logs, metrics, and distributed traces for abnormal behavior.
This integrated approach reduces operational complexity while improving both user experience and defensive capability.
Conclusion
Website speed is more than a usability metric. It reflects the overall health of an application’s architecture, infrastructure, and operational practices.
Performance degradation may indicate aging software, inefficient application design, malicious traffic, or an active security incident. Likewise, many security improvements naturally enhance application responsiveness by reducing unnecessary complexity and strengthening infrastructure.
As modern web applications become increasingly distributed and interconnected, the distinction between performance engineering and cybersecurity continues to diminish.
Organizations that evaluate latency, infrastructure health, and threat activity as components of the same operational picture will detect problems earlier, respond more effectively, and build systems that are both faster and significantly more resilient.