Initial Access Brokers: The Cybercrime Market Behind the First Step of an Attack
CybersecurityModern cyberattacks are increasingly organized as specialized operations rather than being conducted by a single threat actor from beginning to end. One group may steal credentials, another may develop malware, and a third may deploy ransomware or exfiltrate corporate data. Between these stages, there is often a market for one of the most valuable commodities in cybercrime: unauthorized access to a real organization.
This is where initial access brokers (IABs) operate. Their primary objective is not necessarily to steal data or encrypt systems. Instead, they compromise an organization, establish a viable foothold, validate what they have obtained, and sell that access to another criminal group.
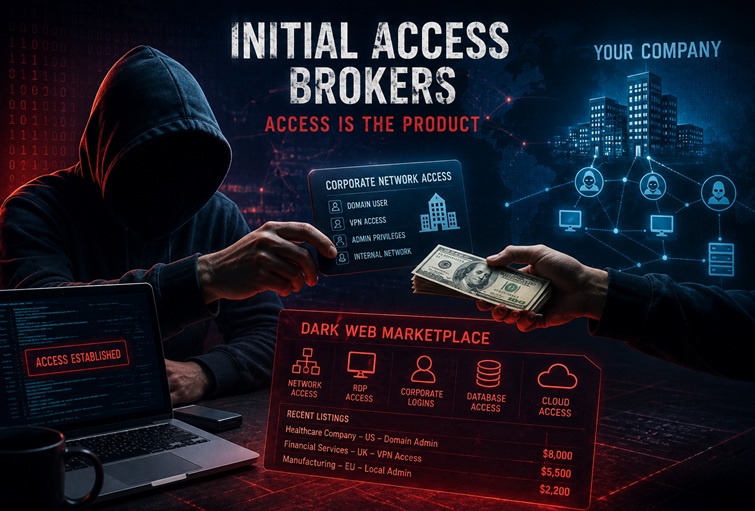
The emergence of IABs has effectively created a cybercrime supply chain. Specialization allows individual actors to focus on the part of an intrusion they perform best, while buyers can acquire access without having to discover and compromise a victim themselves. For defenders, this means that a seemingly minor credential compromise or suspicious remote login can be the first stage of a much larger attack.
What Is an Initial Access Broker?
An initial access broker is a cybercriminal who obtains unauthorized access to an organization and monetizes that access by selling it to other threat actors.
The access can take many forms. It may be a compromised employee account, a valid VPN credential, access to a remote desktop service, a compromised server, a web application account, or a foothold inside a corporate network. In more valuable cases, the broker may obtain privileged credentials or direct access to an enterprise environment.
The broker typically does not need to know exactly what the eventual buyer intends to do. The access itself is the product.
This distinction is important because IABs occupy a different position in the attack lifecycle from ransomware operators, data theft groups, or business email compromise specialists. Their work ends when they have established and verified a sufficiently valuable entry point.
A simplified IAB business model can be described in four stages:
- Compromise: obtain unauthorized access to a target.
- Validation: determine whether the credentials or system access actually works.
- Profiling: establish what organization, systems, privileges, and geographical location are associated with the access.
- Sale: offer the access through criminal marketplaces or private channels.
The buyer can then use the acquired foothold as the starting point for a separate intrusion.
Why Initial Access Has Become a Commodity
The growth of IABs reflects a broader professionalization of cybercrime.
In the past, a criminal group attempting to deploy ransomware might have needed to identify a target, conduct reconnaissance, steal credentials, compromise an exposed service, move through the network, and finally deploy its payload. Today, different specialists can perform these tasks independently.
This model reduces the amount of expertise and infrastructure required by each participant.
For example, a ransomware operator does not necessarily need a sophisticated phishing operation if compromised corporate credentials are already available for purchase. Likewise, a criminal group specializing in data theft can acquire access to an organization without spending weeks attempting to penetrate its perimeter.
The result is an ecosystem in which access, credentials, malware, infrastructure, data and other capabilities can be traded independently.
This specialization also creates an economic incentive for brokers to compromise as many organizations as possible. A successful foothold can be monetized without requiring the broker to conduct the noisy and risky second half of an attack.
What Makes Access Valuable?
Not every compromised account has the same value.
The price and attractiveness of an access opportunity depend on a combination of technical and business factors. These can include:
- The privileges associated with the compromised account
- Whether the account provides remote network access
- The presence of administrative credentials
- The size and type of the victim organization
- The industry in which the organization operates
- The geographical location of the victim
- The number of accessible systems
- Whether security controls such as MFA are present
- Whether the access provides a path into cloud infrastructure
- The apparent presence of valuable data or critical business systems
A compromised account belonging to an ordinary employee may provide limited opportunities. An account capable of accessing a corporate VPN, cloud administration console, virtualization platform, or domain environment can be considerably more useful.
Healthcare, financial services, manufacturing, energy, technology and other sectors with valuable data or operational infrastructure can also be attractive targets.
For this reason, IABs frequently provide buyers with information about the victim and the nature of the access. The more accurately the broker can demonstrate that the access is functional and valuable, the easier it becomes to sell.
How Initial Access Brokers Compromise Organizations
IABs use many of the same techniques employed by other threat actors. What distinguishes them is the business model built around the resulting access.
Stolen credentials and infostealers
Credential theft is one of the most important sources of initial access.
Infostealer malware can collect passwords, browser cookies, authentication tokens and other information from compromised computers. Depending on the malware and the victim’s environment, the stolen information can provide access to corporate applications, email accounts, VPN services and cloud platforms.
Session cookies and authentication tokens can be particularly valuable because they may allow an attacker to bypass some of the normal authentication steps associated with a username and password.
The criminal ecosystem surrounding infostealers also demonstrates how specialized cybercrime has become. One actor may operate the malware infrastructure, another may purchase the stolen credentials, and an IAB may subsequently package access to a corporate environment for resale.
Vulnerable internet-facing systems
Organizations expose numerous services to the public Internet, including VPN gateways, remote desktop infrastructure, web applications, management interfaces and other remote access technologies.
Any vulnerability or configuration mistake affecting these systems can create an entry point.
Delayed patching is particularly dangerous because attackers continuously scan the Internet for vulnerable infrastructure. Once a weakness becomes publicly known and a reliable exploitation method becomes available, organizations that have not patched affected systems can quickly become targets.
Remote Desktop Protocol is another frequent target. Exposing RDP directly to the Internet can create opportunities for password attacks, credential theft and exploitation of vulnerabilities. The same principle applies to other remote access technologies and administrative interfaces.
Phishing and social engineering
Human interaction remains another important route to initial access.
Attackers can create convincing messages designed to persuade employees to disclose credentials, approve authentication requests, open malicious documents or visit fraudulent login pages.
Modern phishing operations can be highly targeted. Attackers may imitate suppliers, customers, colleagues, recruiters or internal departments. Generative AI can further reduce the effort required to create convincing text and adapt messages to particular organizations.
The objective does not necessarily have to be stealing a password directly. An attacker may instead attempt to obtain a session token, convince a user to install remote access software, or establish another form of persistent access.
Compromised third parties
An organization does not necessarily have to be attacked directly.
Suppliers, managed service providers, contractors and other third parties can provide indirect routes into an enterprise environment. If a compromised service provider has privileged connectivity to multiple customers, a single successful intrusion can potentially expose several organizations.
This makes third-party access management an increasingly important component of defenses against IAB activity.
From Initial Access to a Full-Scale Attack
The significance of an IAB foothold becomes apparent when considering what happens after the sale.
An initial compromise may remain dormant for some time. The buyer might first conduct reconnaissance, identify valuable systems, obtain additional credentials and determine how to move through the environment without attracting attention.
The subsequent attack could involve:
- Credential theft
- Privilege escalation
- Lateral movement
- Data exfiltration
- Business email compromise
- Deployment of ransomware
- Destruction or modification of systems
- Extortion
- Installation of persistent backdoors
This creates a major challenge for incident responders. The organization may detect an attack months after the original access was obtained, and the group currently operating inside the environment may have no direct relationship with the actor who initially compromised it.
Consequently, investigating only the most visible stage of an incident can leave important questions unanswered.
Why IAB Activity Is Difficult to Detect
Initial access is often deliberately designed to resemble ordinary activity.
A valid username and password used to connect to a VPN can look legitimate. A stolen session token can allow access without triggering a conventional password-based alert. A compromised employee account may behave normally for weeks before being used for malicious purposes.
The separation between the broker and the eventual attacker makes attribution even harder.
Consider a hypothetical scenario in which an organization is compromised in January. The access is sold in February, but the buyer does not begin using it until May. In June, ransomware is deployed.
The security team investigating the ransomware incident may see activity associated with the second attacker but have limited visibility into the original compromise. The infrastructure, malware and techniques used during the initial intrusion may be completely different from those observed during the final attack.
For this reason, defenders should treat evidence of unauthorized access as a potentially significant security event even when there are no immediate signs of data theft or ransomware.
The Role of Identity Security
The growth of IABs reinforces an important change in enterprise security architecture: identity has become a critical part of the attack surface.
Traditional perimeter defenses assume that unauthorized users can be kept outside the network. Modern environments are considerably more distributed. Employees work remotely, applications are hosted in the cloud, contractors require access to internal resources, and corporate systems communicate with external services.
As a result, an attacker who obtains legitimate credentials may appear to be an authorized user.
Organizations therefore need visibility into authentication behavior, not just malware detection.
Security teams should pay attention to indicators such as:
- Authentication from unusual geographical locations
- Impossible travel patterns
- Logins at unusual times
- Repeated authentication failures followed by success
- Access to applications the user does not normally use
- Unexpected privilege changes
- New authentication methods or devices
- Abnormal VPN activity
- Suspicious use of service accounts
- Large changes in normal account behavior
These signals become particularly valuable when combined rather than evaluated independently.
How Organizations Can Reduce IAB Risk
There is no single control that eliminates the threat posed by initial access brokers. Effective defense requires multiple layers designed to make compromise more difficult and reduce the value of stolen credentials.
Deploy phishing-resistant MFA
Multi-factor authentication can significantly reduce the usefulness of stolen passwords. However, not all MFA implementations provide the same level of protection.
Where possible, organizations should consider phishing-resistant authentication technologies such as FIDO2 security keys or passkeys. These approaches are designed to prevent attackers from simply capturing authentication secrets through conventional phishing pages.
Minimize Internet exposure
Internet-facing systems should be continuously inventoried and reviewed.
Organizations should identify unnecessary services, remove obsolete remote access infrastructure, restrict administrative interfaces and avoid exposing RDP or similar services directly to the public Internet unless there is a compelling reason.
Where remote access is required, it should be protected with strong authentication, access controls, network restrictions and continuous monitoring.
Patch externally exposed systems quickly
Internet-facing vulnerabilities deserve a higher remediation priority than vulnerabilities on isolated internal systems.
Asset inventories, vulnerability scanning and automated patch management can help organizations identify exposed infrastructure before attackers do.
Protect credentials and sessions
Endpoint protection should be complemented by identity monitoring and controls designed to reduce credential theft.
Organizations should also consider conditional access policies, device compliance checks, privileged access management and short-lived authentication mechanisms where appropriate.
Monitor identity behavior
Traditional endpoint detection remains important, but it should not be the only source of visibility.
Security teams need to understand who is accessing corporate resources, from which devices, from which locations and under what circumstances. Detecting anomalous identity activity can expose a compromised account even when no malicious executable is present.
Segment critical infrastructure
Network segmentation can limit the consequences of a successful initial compromise.
An attacker who obtains an ordinary employee account should not automatically be able to reach domain controllers, production systems, backup infrastructure or sensitive databases.
Segmentation, least-privilege access and carefully controlled administrative pathways can turn a successful initial intrusion into a contained security incident rather than an organization-wide compromise.
Prepare for stolen credentials
Organizations should assume that some credentials will eventually be exposed.
Incident response procedures should therefore include mechanisms for rapidly disabling compromised accounts, revoking active sessions, rotating credentials, reviewing authentication logs and investigating devices associated with suspicious activity.
Speed matters. The period between initial compromise and detection can determine whether an attacker remains isolated or gains access to critical systems.
IABs Are a Symptom of a Larger Transformation
Initial access brokers are not simply another type of cybercriminal. Their growth demonstrates how the cybercrime economy has become increasingly specialized.
Access has become a product that can be discovered, validated, priced and resold. This allows ransomware operators, data theft groups and other criminals to outsource one of the most difficult stages of an attack.
For defenders, the implication is straightforward. A compromised credential, suspicious VPN connection or vulnerable Internet-facing server should not automatically be treated as an isolated technical problem. It may represent the first stage of an intrusion whose most damaging consequences have not yet occurred.
The most effective strategy is therefore to focus on preventing initial compromise, detecting abnormal identity activity as early as possible, and limiting what a compromised account can reach.
IABs make cybercrime more efficient by turning access into a commodity. Organizations can counter that advantage by making access harder to obtain, harder to abuse and far less valuable when compromised.